"We are a startup, so the 24-hour reporting deadline does not apply to us." This sentence has been making the rounds in founder circles since 11 September 2026, and it is more dangerous than most myths about the Cyber Resilience Act (EU CRA): it is not invented out of thin air, it is a misreading of a real provision. That is exactly why it sticks. This post shows what the startup relief in the EU CRA actually delivers, and what it does not.
What does the exemption in Article 64(10) actually say?
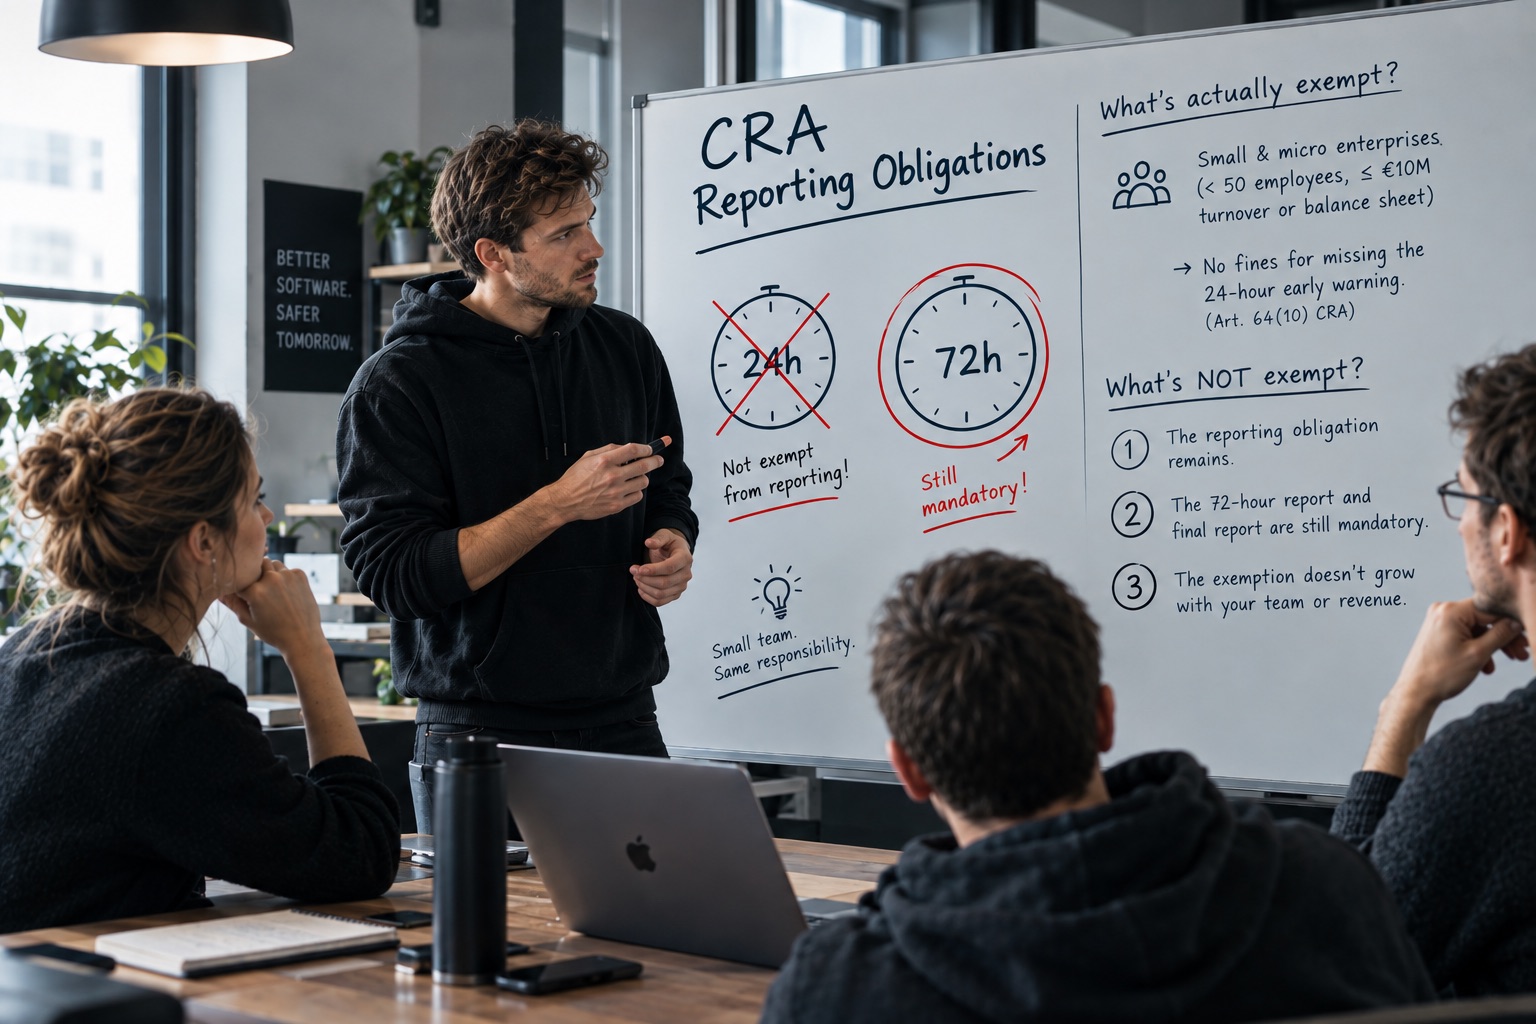
The EU Cyber Resilience Act does contain a relief for small manufacturers. Article 64(10) exempts microenterprises (fewer than 10 employees, at most 2 million euros in turnover or balance sheet total) and small enterprises (fewer than 50 employees, at most 10 million euros) from fines when they miss one very specific deadline: the 24-hour early warning under Article 14(2)(a) and Article 14(4)(a). It is part of a small package of SME relief measures in the EU CRA.
Article 64(10) of the Cyber Resilience Act contains nothing beyond that: the provision covers only the fine for a late early warning. Three things are not in it:
- The reporting obligation itself does not go away. Actively exploited vulnerabilities and severe incidents must be reported via the Single Reporting Platform, even by a five-person team. What exactly is reportable is set out in Article 14 of the Cyber Resilience Act.
- The 72-hour notification and the final report are not covered. The exemption only reaches the early-warning stage. Anyone who takes their time there still owes the full detailed notification three days later.
- The relief does not grow with you. From 50 employees or 10 million euros in turnover, it is gone. On top of that, company size already factors into how fines are calculated; that is proportionality at work, not a waiver of the obligation.
Why is this misreading especially expensive for startups?
Picture a twelve-person IoT startup that learns on Tuesday that a vulnerability in its gateway is being actively exploited. A late early warning carries no fine for this team. A late 72-hour notification on Friday does. And if the team has no reporting process on Tuesday, it will not have one by Friday either. Both clocks start the moment you become aware, as described in the post on the 24-hour deadline running from awareness.
Then there is the real risk that no penalty clause captures: for a young company with its first enterprise customers, a badly managed security incident is a bigger threat to survival than any fine. The customer who asks about your reporting process in a supplier audit will not accept "we are under 50 people" as an answer. And anyone who builds their process on the exemption has to rebuild it from scratch once they grow past the threshold, typically at exactly the moment when everything else is happening at once. That the regulation spares no size class overall is something I covered in the post on why mid-sized manufacturers are fully in scope.
Myth vs. Fact
Myth: Startups and small manufacturers are exempt from the reporting obligation of the EU CRA and from the 24-hour deadline.
Fact: Under Article 64(10) of the EU Cyber Resilience Act, micro and small enterprises are only exempt from fines for missing the 24-hour early warning. The reporting obligation itself, the 72-hour notification and the final report apply in full, and the relief ends at 50 employees or 10 million euros.
Concrete consequences for small teams
1. Treat the exemption as an airbag, not as a driving style. Plan your reporting process as if the fine waiver did not exist. It is the safety net for when something goes wrong despite preparation, not the justification for having no preparation.
2. Build the lean version; it is enough. Article 14 is very manageable for small teams: one person responsible for reporting plus a deputy, prepared templates for the early warning and the detailed notification, a defined intake channel for reports, one dry run. That is a few person-days, not a compliance department. The full guide with a deadline table and checklist is in the article on the EU CRA reporting obligation.
3. Document your size class and watch the threshold. Record the basis on which you classify yourself as a micro or small enterprise, and revisit it with every growth step. The classification does not decide your obligations, but it decides your residual risk, and it goes stale faster than a funding round closes.
What does this mean for your EU CRA roadmap?
Since 11 September 2026, the reporting obligations under Article 14 of the EU Cyber Resilience Act apply, including to the smallest manufacturers. From 11 December 2027, the full application of the EU CRA follows, with conformity assessment and CE marking, and there is no comparable size exemption there. Build the lean reporting process now and you have laid the groundwork for 2027. The overall plan is laid out in the CRA roadmap 2026/2027, the sanctions logic in the article on fines and penalties. What the EU CRA means for small and mid-sized manufacturers beyond reporting is bundled on the overview page EU CRA for SMEs.
Frequently asked questions
We are a team of 8. Do we really have to report? Yes. The reporting obligation under Article 14 of the EU Cyber Resilience Act applies regardless of company size. Your size class only affects the fine risk for a missed 24-hour early warning, not whether the obligation exists.
Does the exemption count per company or per group? What matters are the SME criteria of EU Recommendation 2003/361/EC, and those count linked enterprises. A small subsidiary of a large group will usually not qualify for the relief. When in doubt, this question belongs with your lawyer.
Does the relief also cover the notification of severe incidents? It covers the 24-hour early-warning stage of both notification types (Article 14(2)(a) and Article 14(4)(a) EU CRA), but not the respective 72-hour notifications and final reports.
What happens if we grow past the threshold during an ongoing case? The classification is not a snapshot of a single day; it follows the SME criteria with their reference periods. Do not rely on edge cases: anyone close to the threshold should operate as if they were above it.
Conclusion
The startup relief in the EU Cyber Resilience Act is real, but small: no fine for a missed early warning, nothing more. Turning that into "we are exempt" confuses an airbag with a driving licence. The good news: for small teams, Article 14 is the most manageable part of the EU CRA if you set it up lean.
Our startup programme exists for exactly this, with special terms for companies under 50 employees: reporting process, deadline tracking and documentation in one place, before the first real incident turns theory into practice. The free CRA assessment is the place to start. And next week you can meet us in person at Bits & Pretzels in Munich.
Every Friday I debunk a CRA myth here.